Solution Builders team
Jump to a section
- Attackers detonate on Friday nights and in tax season on purpose. Maximum pressure to pay, minimum people watching the console.
- Behavior based XDR isolated the laptop in two minutes and a human analyst was engaged in eight. The 22 minutes were preparation, not luck.
- Immutable backups meant the encrypted folders rolled back from a snapshot nobody could touch. Restore took one afternoon, not three weeks.
- No ransom, no client notifications, no insurance claim. The incident report became proof of a working program at renewal.
Friday at 6:41 p.m., somebody clicked
Every accounting firm in the Twin Cities has the same soft spot: a senior associate, an inbox full of client documents and a deadline. Ransomware crews know it, which is why they time detonations for nights and weekends, when internal IT has gone home and nobody is watching the console. A Friday evening in tax season is the perfect window, with maximum pressure to pay and minimum people on hand. Ransomware recovery in Minneapolis is usually a story about Monday morning phone calls. This one is about a Friday night phone call that said it was already over.
The firm, a 42 user accounting and advisory practice with one office and hybrid staff, had engaged Solution Builders eighteen months earlier for managed security after a cyber insurance renewal demanded multifactor authentication, endpoint detection and tested backups. Those controls were about to earn their keep.
- Entry point. A phishing email with a weaponized invoice attachment that looked like it came from a long time client.
- Target. The file server and the client document library.
- Controls in place. MFA, managed XDR, a 24/7 MDR team and an immutable backup.
- Insurance. A policy renewed on the strength of those controls.
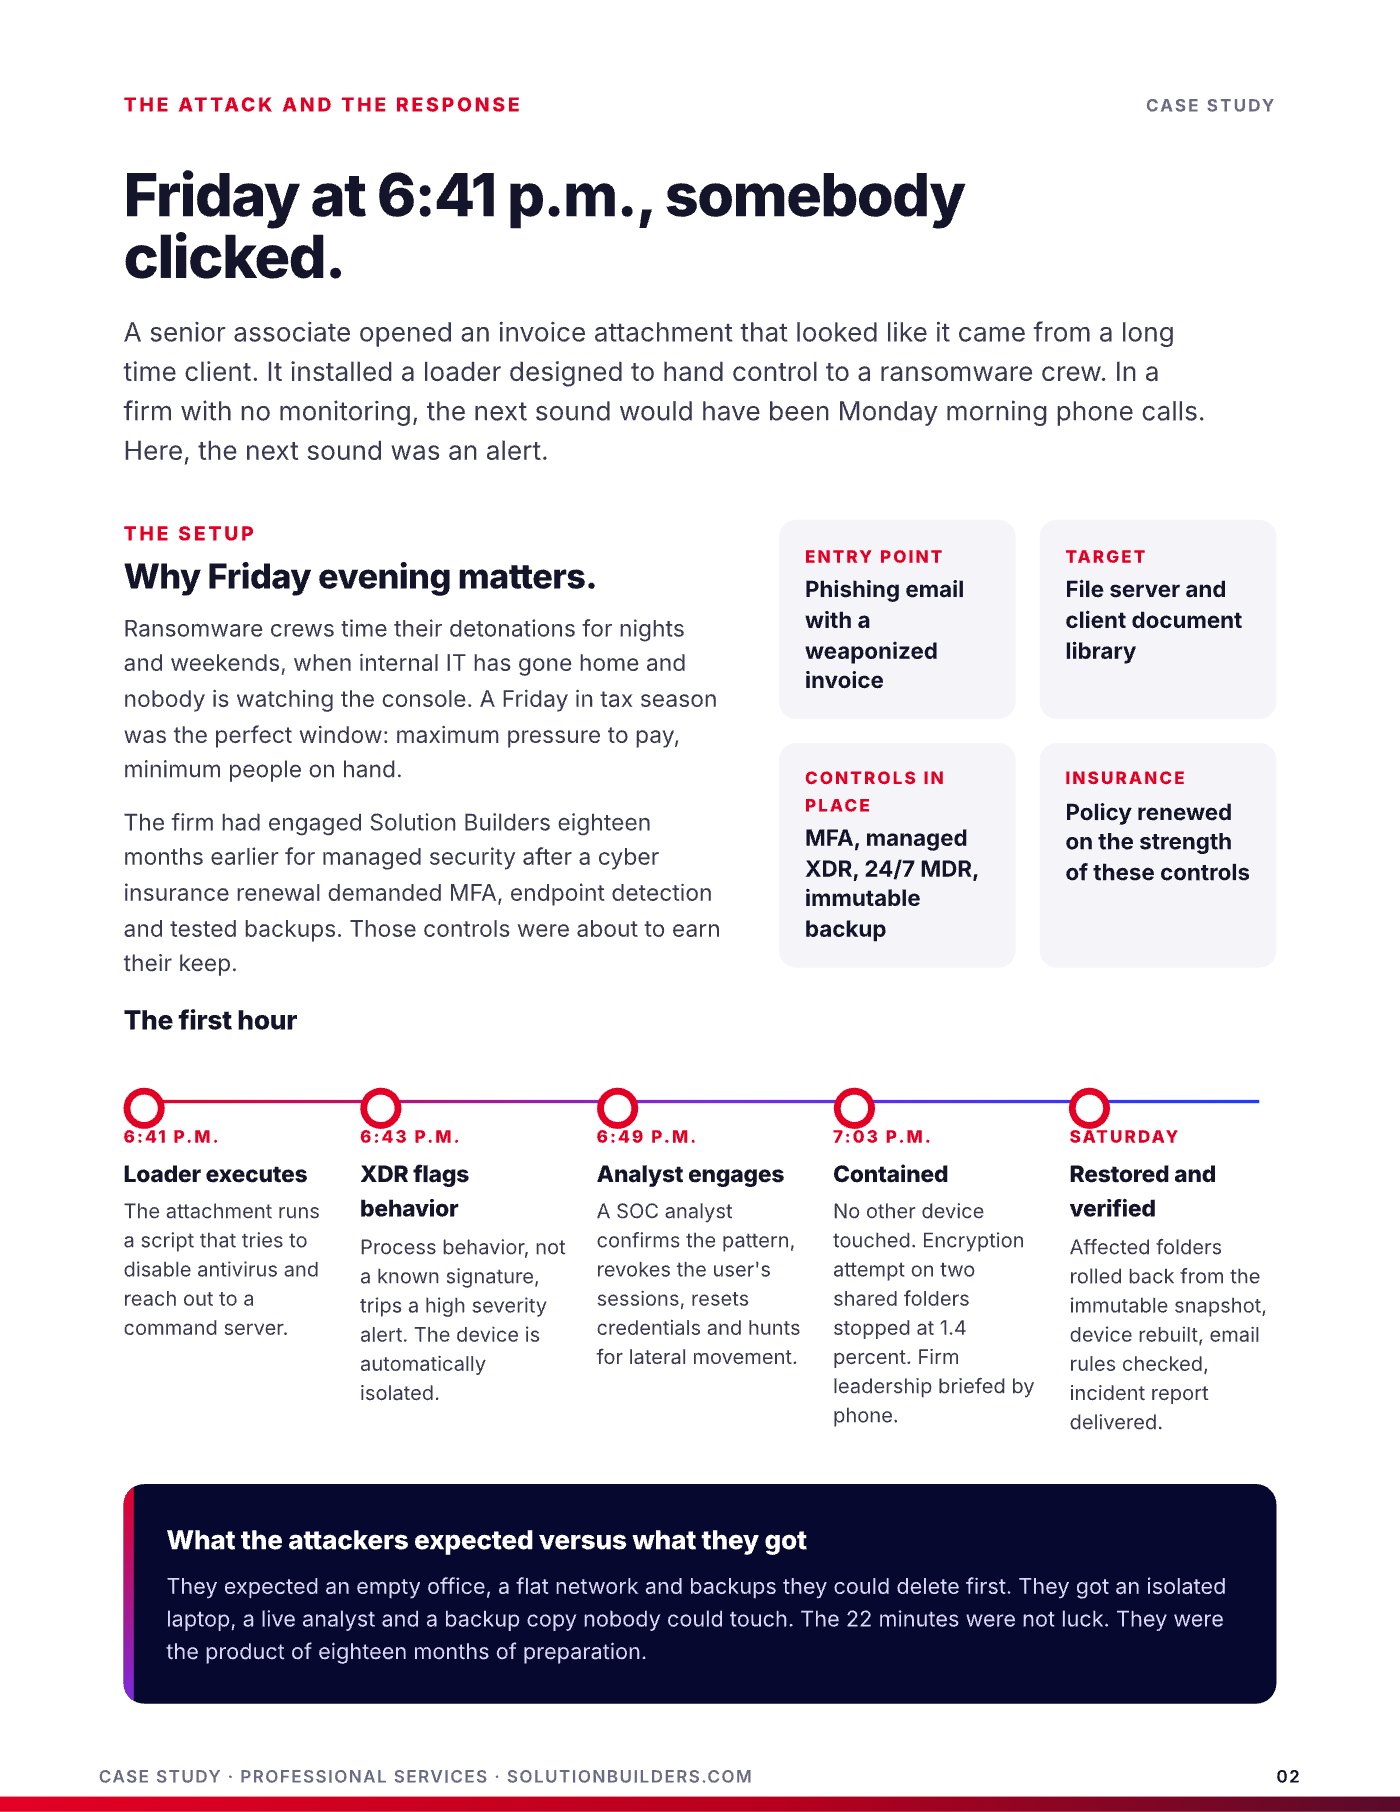
The 22 minute timeline, minute by minute
The attachment installed a loader designed to hand control to a ransomware crew. In a firm with no monitoring, the next sound would have been Monday morning phone calls. Here, the next sound was an alert.
- 6:41 p.m., loader executesThe attachment runs a script that tries to disable antivirus and reach out to a command server.
- 6:43 p.m., XDR flags behaviorProcess behavior, not a known signature, trips a high severity alert. The device is automatically isolated from the network.
- 6:49 p.m., analyst engagesA security operations center analyst confirms the pattern, revokes the user's sessions, resets credentials and hunts for lateral movement.
- 7:03 p.m., containedNo other device touched. An encryption attempt on two shared folders stopped at 1.4 percent. Firm leadership briefed by phone.
- Saturday, restored and verifiedAffected folders rolled back from the immutable snapshot, the device rebuilt, mailbox rules checked, incident report delivered.
Preparation, not luck
They expected an empty office, a flat network and backups they could delete first. They got an isolated laptop, a live analyst and a backup copy nobody could touch. The 22 minutes were the product of eighteen months of preparation.
Managed detection and response: why this story ended differently
Coveware and Sophos reporting commonly puts downtime from an SMB ransomware incident at about three weeks. This firm lost half a day, on a weekend. The difference was not one product. It was five controls that had been installed, tested and watched for a year and a half before anyone needed them.
| Control | Role in the incident | Without it |
|---|---|---|
| Managed XDR | Detected behavior in 2 minutes, isolated the device automatically | Loader runs all weekend |
| 24/7 MDR SOC | A human analyst engaged within 8 minutes on a Friday night | Alert sits in an inbox until Monday |
| Immutable backup | Snapshot could not be encrypted or deleted, restore took one afternoon | Backups deleted first, ransom is the only option |
| MFA and conditional access | Stolen credentials could not be reused from outside | Attacker logs in as the associate |
| Email protection | Blocked the attacker's follow up messages to other staff | Second and third victims |
Two of those rows deserve a closer look. Managed detection and response is the human half of XDR: the platform raises the alert, and a person in a 24/7 security operations center with authority to act decides what to do in the next five minutes. And immutable backups are the reason the ransom question never came up. Sophos has reported that attackers try to compromise backups in the large majority of ransomware cases, so a backup that cannot be altered or deleted, even by an administrator, is the control that turns a crisis into a restore job.
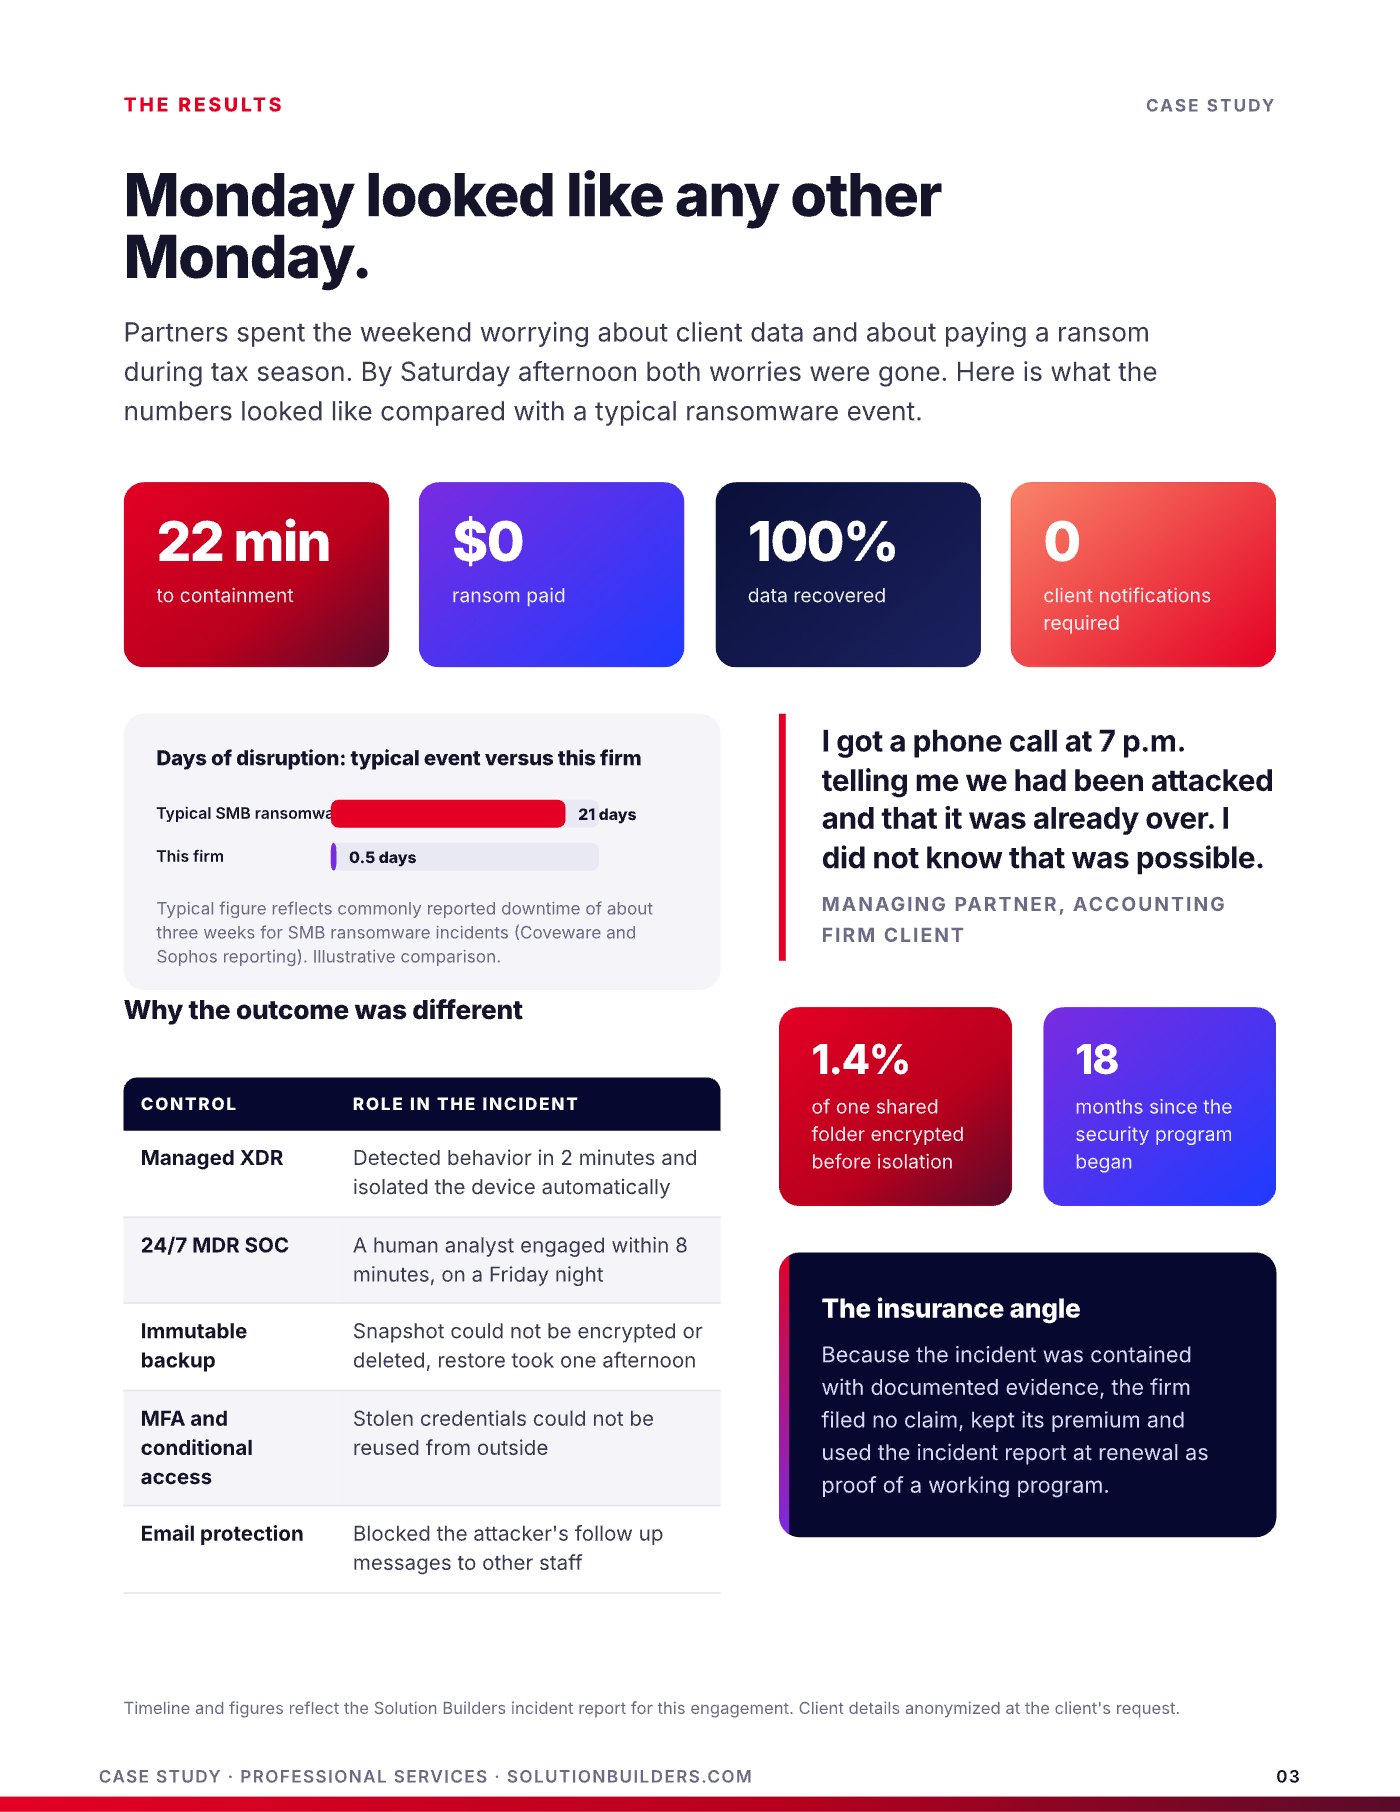
Monday looked like any other Monday
Partners spent Friday night worrying about client data and about paying a ransom in the middle of tax season. By Saturday afternoon both worries were gone. The firm filed no insurance claim, kept its premium and used the incident report at renewal as proof of a working program.
I got a phone call at 7 p.m. telling me we had been attacked and that it was already over. I did not know that was possible.Managing Partner, Solution Builders accounting firm client
Zero client notifications is the number the partners remember. Nothing left the building, so there was no breach to disclose, no letters to write and no awkward conversation with the firm's largest clients in the busiest month of the year.
What every Twin Cities accounting firm should copy
Firms with 25 to 500 people in Minneapolis and St. Paul hold exactly what attackers want: tax returns, bank details and the trust of every client. The lessons from this incident are not exotic, and most of them start with a cyber insurance questionnaire.
- Treat the insurance checklist as the floor. MFA, endpoint detection and tested backups are the minimum. This firm started there and kept going.
- Buy the human, not just the tool. XDR raised the alert. An analyst contained it. Ask any provider who is watching at 6:49 p.m. on a Friday.
- Make backups untouchable. Immutable snapshots with quarterly restore tests, so recovery is a procedure, not a prayer.
- Plan for tax season. Attackers time attacks to your busiest weeks. Your controls have to work when nobody is in the office.
Finds out Monday
- Antivirus with nobody watching
- Backups on the same network, deleted first
- Three weeks of disruption and a ransom decision
Finds out at 6:43 p.m.
- Behavior based XDR with a 24/7 analyst
- Immutable backup nobody can touch
- Half a day, no ransom, no notifications
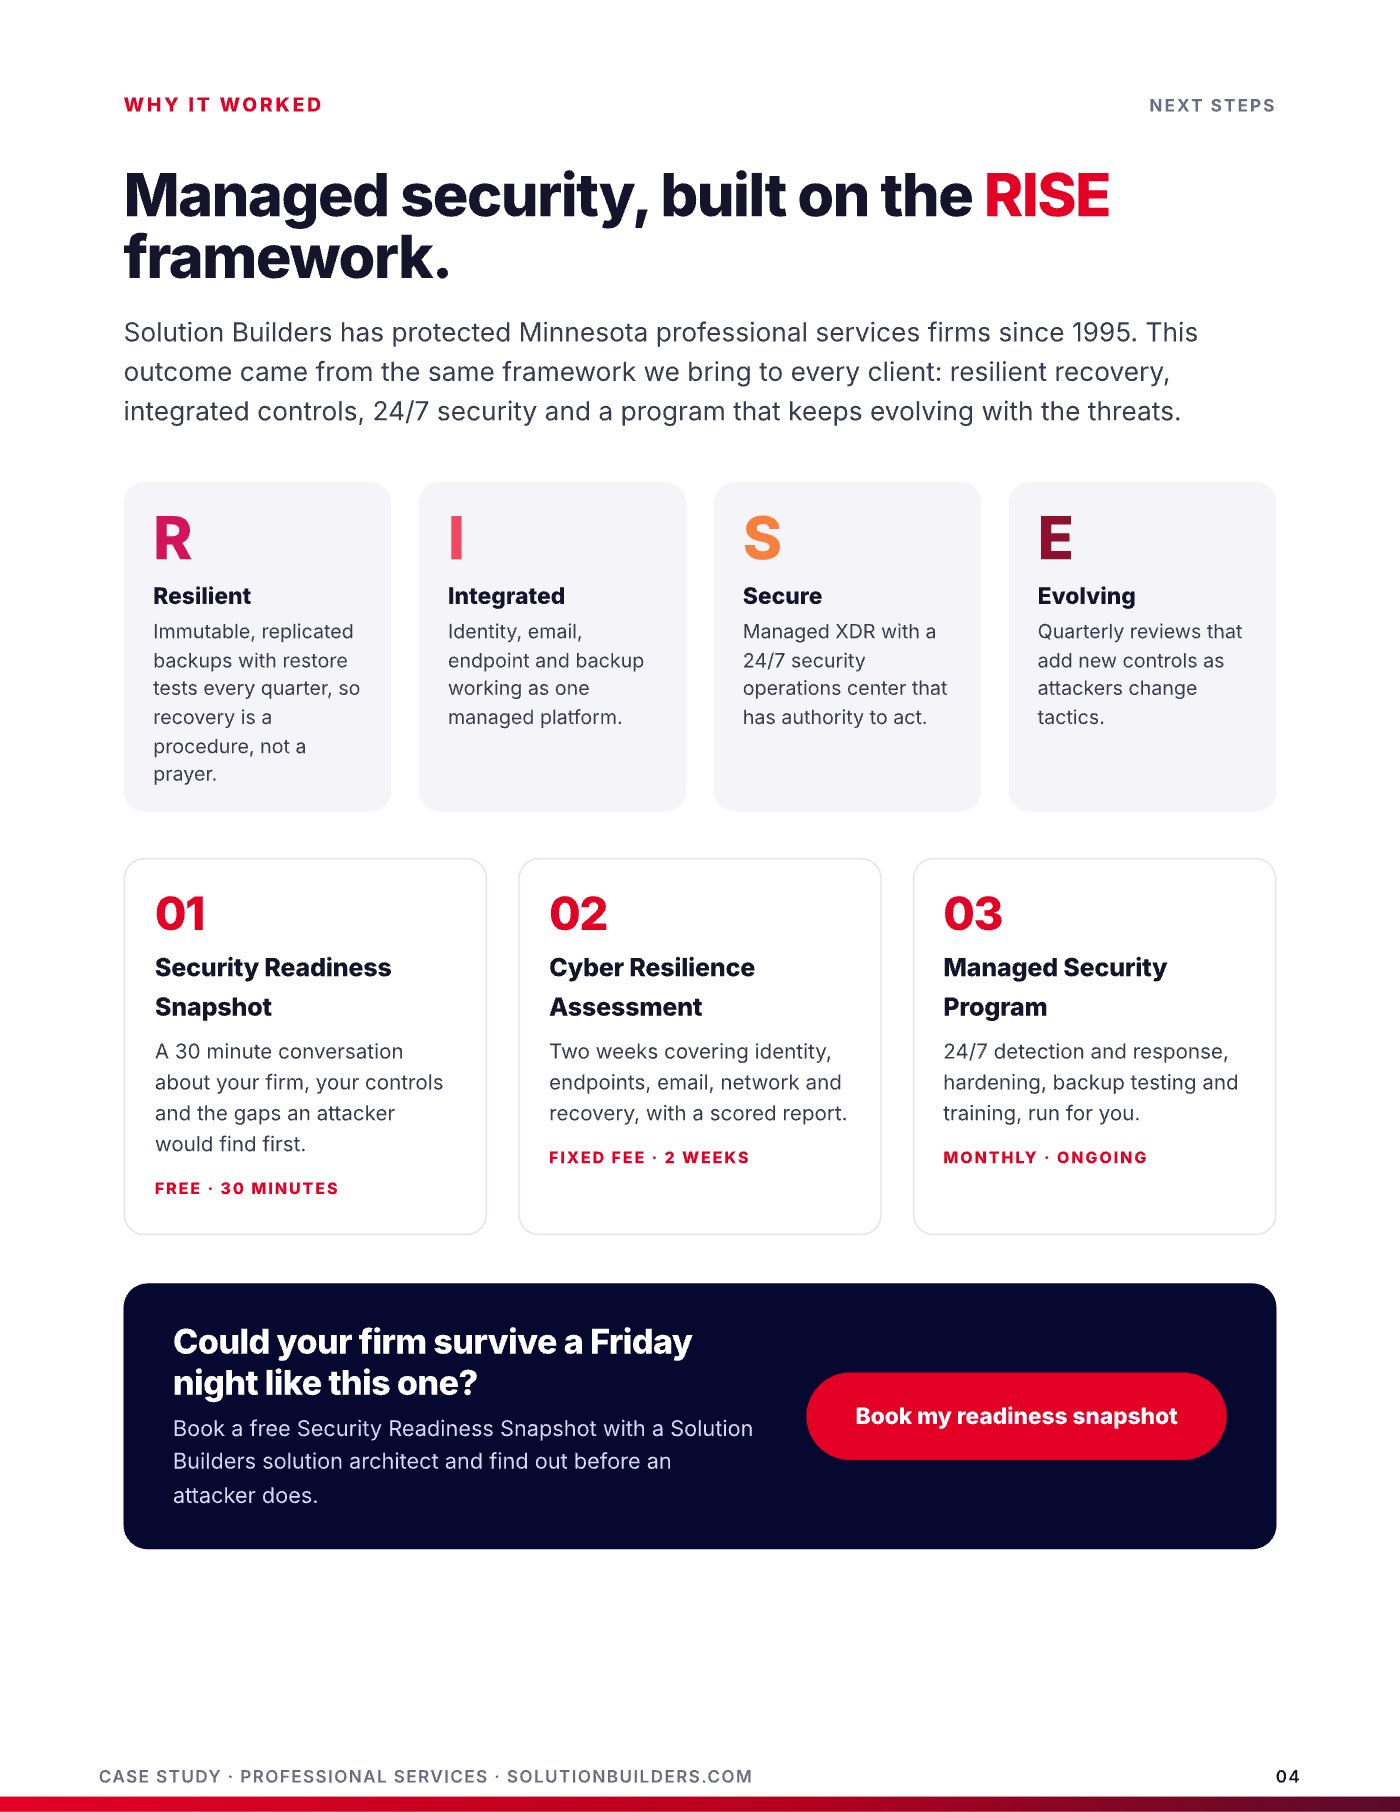
Solution Builders runs this program for accounting firms across the Twin Cities on the RISE framework: resilient recovery, integrated controls, 24/7 security and quarterly reviews that add new controls as attackers change tactics.
Ransomware recovery in Minneapolis starts before your own Friday night
Six things to check this week. If any answer is no, that is the gap an attacker will find first.
- Multifactor authentication is enforced on every account, including email and remote access.
- Every laptop and server runs behavior based detection, not just signature antivirus.
- A named human team watches those alerts 24/7 and has written authority to isolate a device.
- Backups are immutable and off network, and a restore was tested in the last quarter.
- Conditional access blocks sign ins from places your staff never are.
- You have a free 30 minute Security Readiness Snapshot on the calendar with Solution Builders.
Solution Builders has protected Minnesota professional services firms since 1995 from Bloomington, with 50+ engineers, a SOC 2 Type II audited practice and a 24/7 security operations center that handled this incident. The snapshot is a candid conversation about your firm, your controls and the gaps an attacker would find first, whether or not you ever work with us.
Ransomware protection for Twin Cities professional services firms
Solution Builders protects accounting, legal and advisory firms with 25 to 500 people across Minneapolis, St. Paul and the metro from Bloomington. The client in this story is anonymized at its request. Its controls, its 24/7 response team and its immutable backups are the same program we run for every professional services client. Related services: Cybersecurity, Data Backup and Disaster Recovery, Microsoft 365. Contact us or book a 30 minute call.